About the session
The recent Cybersecurity breaches that involved compromised components in software products require all of us to ensure the integrity of the internal and external software libraries used in the software we release. We need to endure that the components and, therefore, the integrated product is Non-GMO Software (please do not Google this as I came up with the term this morning!)
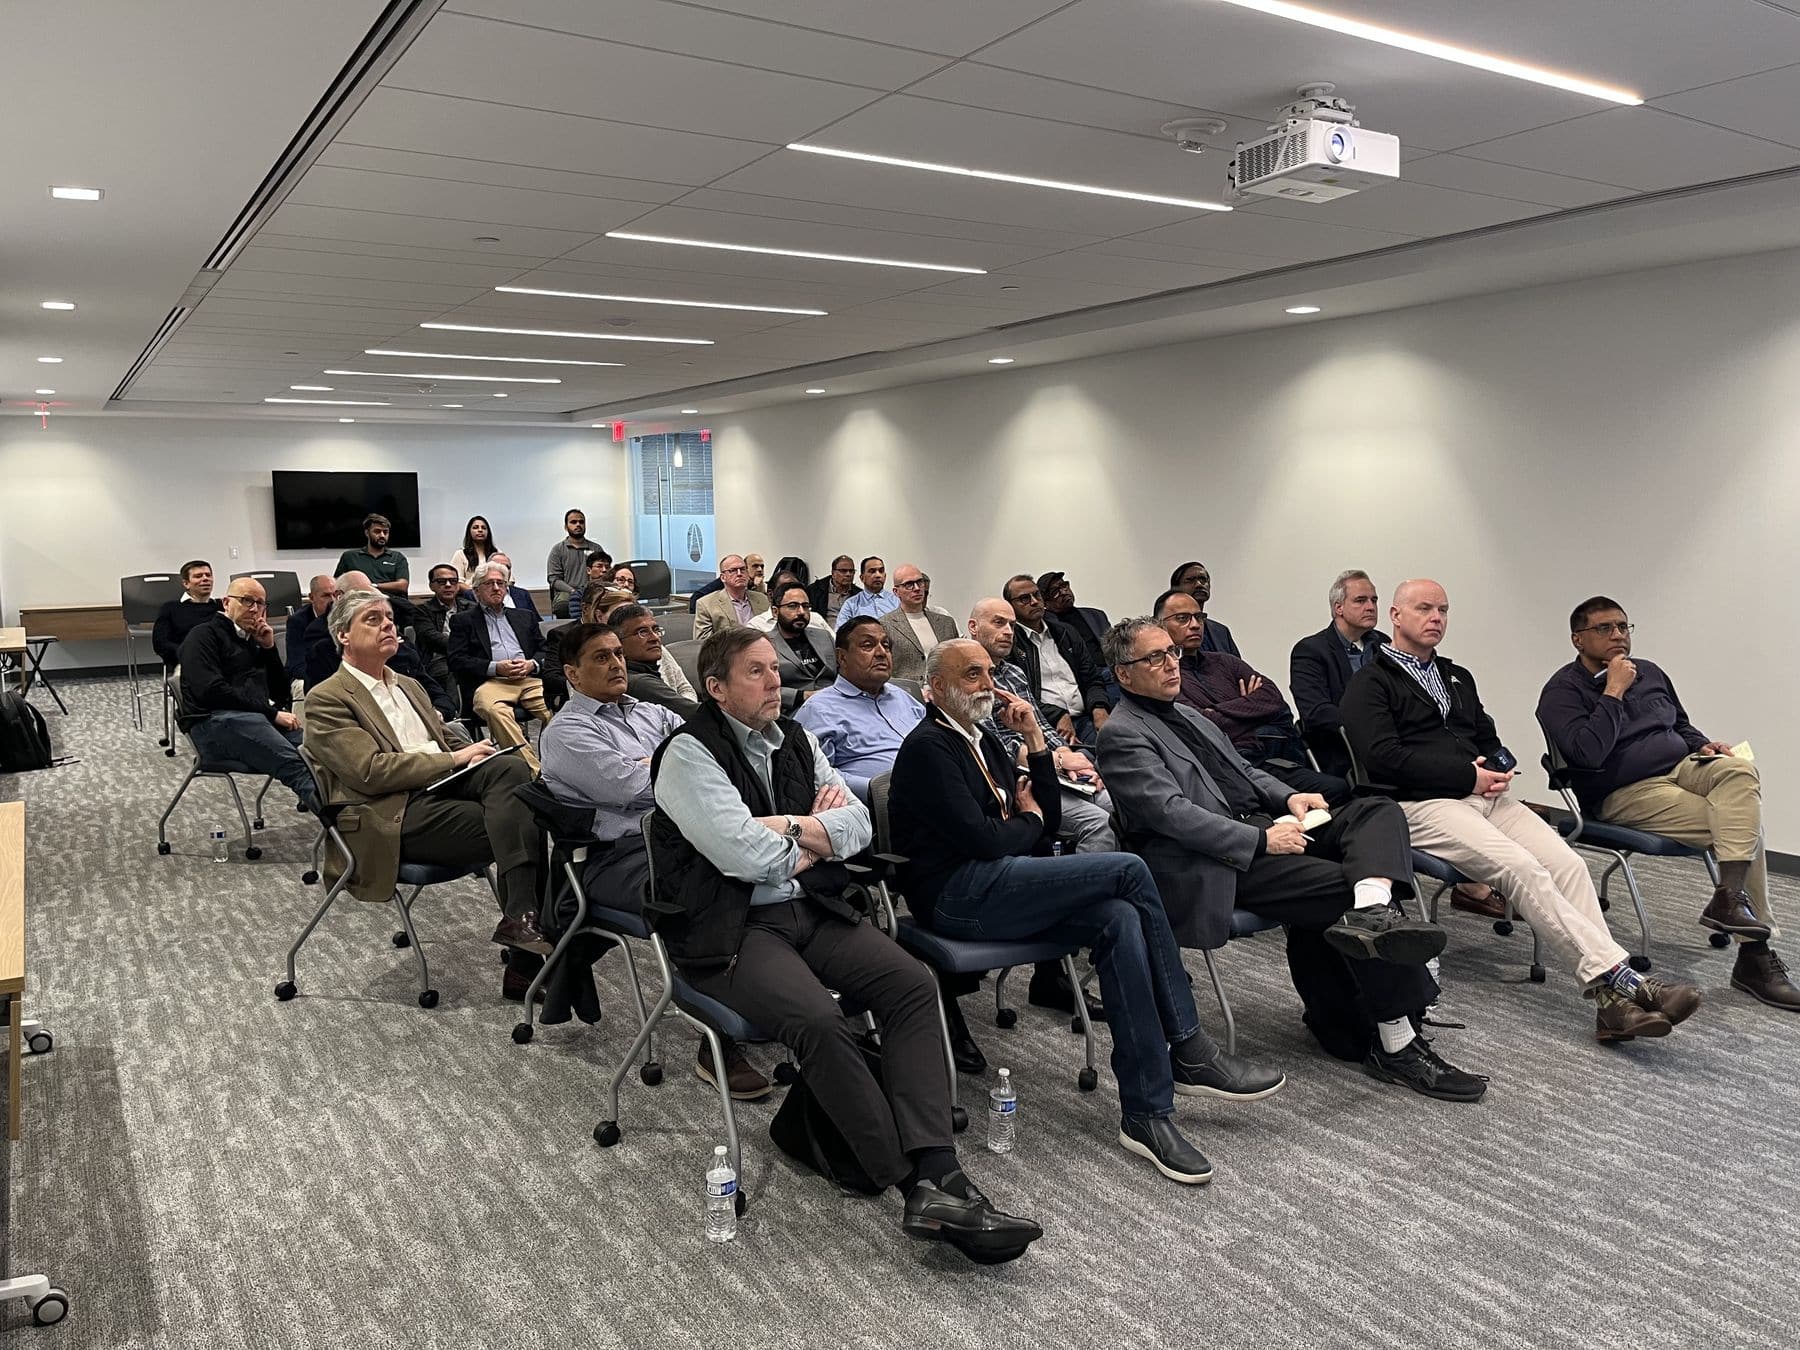
With Solar Winds and Log4j still on many minds, Software Bills of Materials (SBOM) are critical to identify potential underlying gaps in securing your enterprise. During this meeting, we reviewed what an SBOM is and why it is important. We also discussed the importance of:
Requesting SBOMs from your partners and
Including SBOMs with all the software you deliver to your partners and clients
We initiated the discussion with Allan Friedman from CISA setting the stage and spoke about the Federal government’s SBOM efforts.
Eric Schvimmer then presented an overview of how Bloomberg managed the Log4j vulnerability and outline their SBOM activities.
Finally, Dan Tejada from Cantada provided an overview of SBOM generating tools and demoed Cantada’s SBOM generation capabilities.